
Catenaa, Saturday, September 26, 2026- New quantum-computing research has sharply reduced estimates of the hardware needed to attack Bitcoin signatures, strengthening calls for the network to begin preparing for post-quantum security.
The issue was highlighted at BTC Prague in June by CryptoSnake founder Fred King, who presented three possible futures for Bitcoin under advancing quantum technology.
King divided the threat into optimistic, moderate and critical scenarios rather than predicting a date when Bitcoin’s cryptography would fail.
His central concern was whether Bitcoin could coordinate an upgrade before quantum hardware became powerful enough to attack its existing signature system.
Research published during 2026 has made that question harder to dismiss.
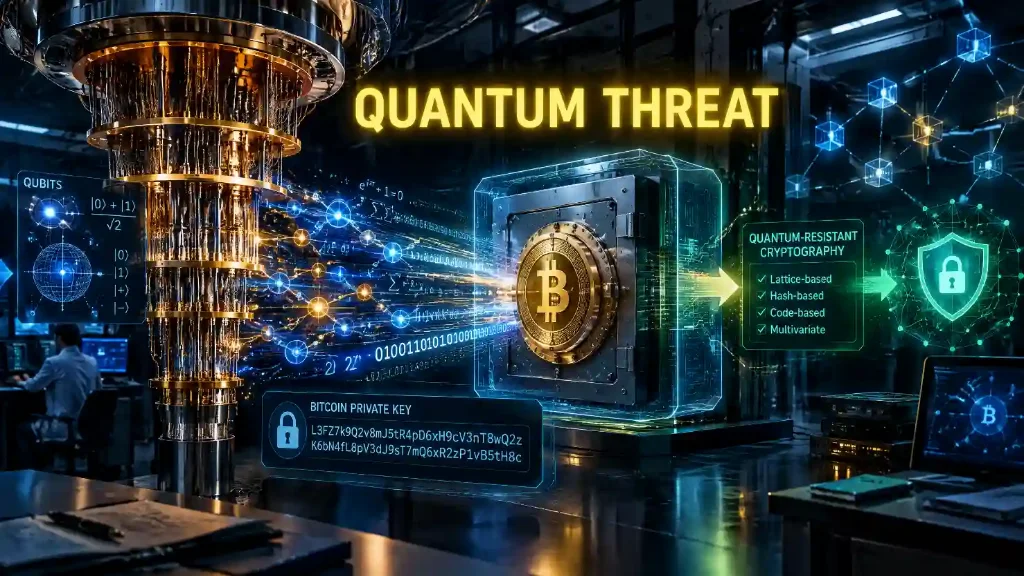
Bitcoin uses the secp256k1 elliptic curve to authenticate ownership and authorize transactions. A sufficiently capable quantum computer running Shor’s algorithm could theoretically derive a private key from its corresponding public key.
That would allow an attacker to create a valid signature and spend bitcoin controlled by the compromised key.
No existing quantum computer can perform such an attack.
However, estimates of the resources needed have fallen rapidly.
Google Quantum AI researchers reported in March that the secp256k1 problem could be solved with either about 1,200 logical qubits and 90 million Toffoli gates, or 1,450 logical qubits and 70 million gates.
After accounting for error correction, Google estimated that a superconducting system using fewer than 500,000 physical qubits could execute the computation in minutes.
The researchers also examined a faster attack against Bitcoin transactions waiting for confirmation.
Part of the quantum calculation could theoretically be completed before a victim’s public key becomes available.
Once the transaction enters Bitcoin’s public mempool, the attacker could finish the remaining computation in about nine minutes under Google’s assumptions.
Bitcoin produces a block roughly every 10 minutes on average.
Google calculated that such an attacker would have just under a 41% chance of completing the attack before a block arrived under its modeled conditions.
That machine does not exist, and the estimate depends on hardware performance and error correction that have not been achieved at the required scale.
A slower threat already matters for coins whose public keys are visible permanently on the blockchain.
Google estimated that about 6.9 million BTC fall into that category.
The total includes early pay-to-public-key outputs, Taproot holdings and funds at addresses where previous spending or address reuse has exposed the public key.
About 1.7 million BTC sit in early pay-to-public-key outputs associated with the Satoshi-era mining period.
Those coins present one of Bitcoin’s hardest future problems because many may belong to owners who have lost their private keys and therefore cannot move them voluntarily.
Another March study from researchers linked to Caltech and quantum company Oratomic attracted attention by lowering the physical-qubit requirement much further.
It showed that Shor’s algorithm could operate at cryptographically relevant scale using as few as 10,000 reconfigurable neutral-atom qubits.
That figure should not be interpreted as a 10,000-qubit machine capable of instantly emptying Bitcoin wallets.
The researchers modeled a different hardware architecture and used the P-256 elliptic curve for their detailed timing estimate rather than Bitcoin’s secp256k1.
Their work showed the tradeoff between machine size and speed. A neutral-atom system using tens of thousands of qubits could require days rather than minutes to solve an elliptic-curve key.
A newer study has now brought the lower-qubit argument directly to Bitcoin.
IonQ researchers reported on September 8 that a proposed fault-tolerant trapped-ion computer using 19,397 physical qubits could solve the secp256k1 problem in about 25.7 days per attempt.
The design uses about 1,457 logical qubits and 39 million Toffoli gates.
IonQ described the work as a resource estimate rather than an attack demonstration.
No such 20,000-qubit fault-tolerant machine currently exists.
The distinction between fast and slow quantum computers is important for Bitcoin.
A slow machine could attack coins whose public keys are already visible because it could spend days or months recovering an individual private key.
A fast machine creates a wider problem because almost every ordinary Bitcoin spend eventually reveals information needed to verify the transaction.
Bitcoin mining itself faces a different quantum problem.
Shor’s algorithm targets the elliptic-curve mathematics protecting ownership. Bitcoin’s SHA-256 hashing system is not broken in the same way.
The emerging debate is therefore centered on signatures and wallet ownership rather than the immediate destruction of Bitcoin’s blockchain.
Work on possible defenses has begun.
BIP 360 proposes a Pay-to-Merkle-Root output type designed to reduce long-exposure quantum attacks by avoiding the vulnerable Taproot key-spend path.
BIP 361 proposes a longer migration process that could eventually restrict legacy ECDSA and Schnorr signatures after users have time to move funds.
Both remain drafts. Neither represents an activated Bitcoin upgrade.
That is where King’s BTC Prague argument becomes most relevant.
The mathematics for post-quantum signatures already exists. NIST approved its first post-quantum cryptographic standards in 2024.
Bitcoin’s harder problem may be coordinating developers, miners, exchanges, custodians, wallet providers and millions of holders around a migration plan.
BlackRock reached a similar conclusion in its July analysis, describing Bitcoin’s post-quantum transition as technically achievable but likely to require several years of coordination.
The quantum threat therefore does not mean Bitcoin is about to be broken.
It means the time available to prepare cannot be measured simply by asking when a quantum computer will arrive.
The other clock is how long Bitcoin itself will need to change.




